Turning Cloud Alert Fatigue into a Small Set of Actionable Detections

Most cloud security teams are drowning in alerts from workload protection, identity, and network tools. The practical fix is not better tuning of every individual rule.
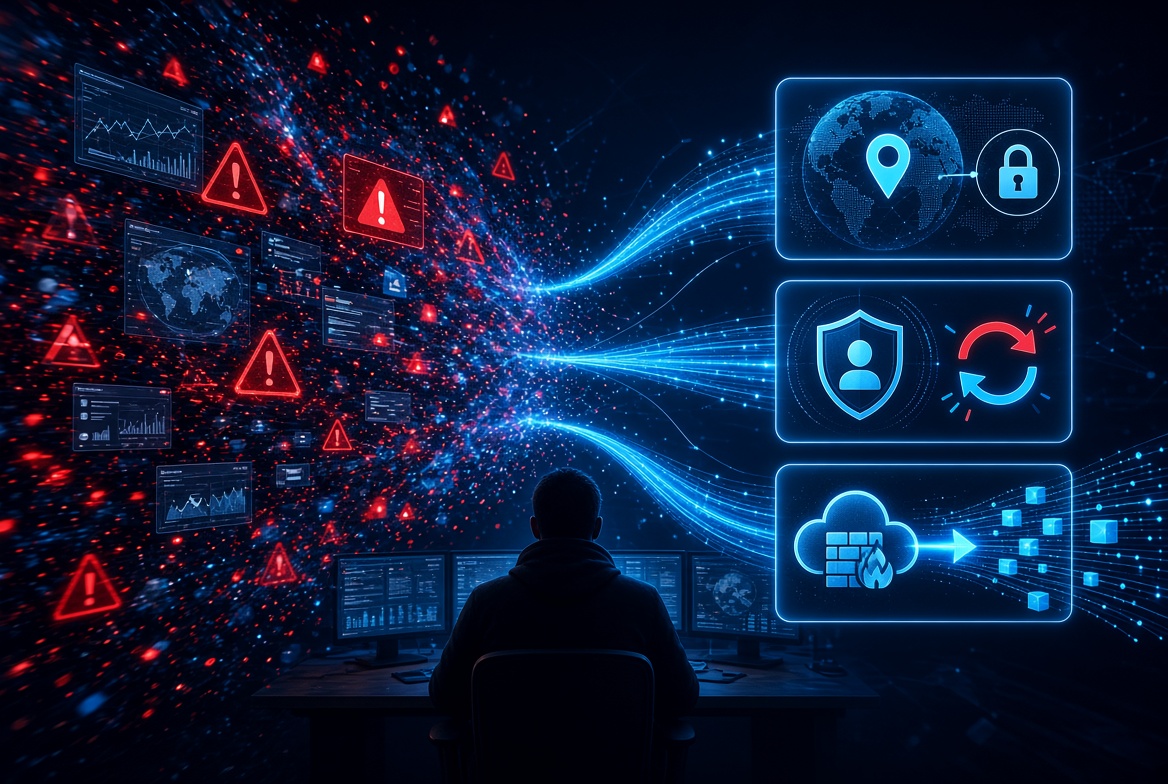
Most cloud security teams are drowning in alerts from workload protection, identity, and network tools. The practical fix is not better tuning of every individual rule. It is collapsing the noise into a handful of high-signal detections that map to real attacker behavior.
Three patterns that consistently produce useful work:
- Identity used from a new location or ASN that then touches a high-value resource within a short window. This catches both stolen credentials and compromised cloud VMs. The exact KQL or detection logic varies by platform, but the idea is the same: first-time geo or ASN + sensitive action = investigate.
- Service principal or managed identity that suddenly starts calling APIs it has never called before. These identities are often over-permissioned and rarely monitored. A simple baseline of normal API calls per identity, then an alert on deviation, surfaces a large percentage of real incidents.
- Resource that is modified and then immediately used for data movement. Creating a new storage account, changing a firewall rule, or granting a new role, followed within minutes by large outbound traffic or bulk data access, is a classic pattern. Correlate the control-plane change with the data-plane activity.
Once you have these three (or similar) running with low false-positive rates, you can safely lower the priority of most individual product alerts. The team’s daily work becomes “review the three high-signal detections and the handful of things they surface,” which is sustainable. Everything else can be sampled or reviewed weekly.