Endpoint Reality: What Still Works When Half Your Devices Are Not Fully Managed

Fully managed, fully compliant devices are the ideal. In most environments a meaningful percentage of endpoints are only partially managed, contractor devices, or simply not enrolled.
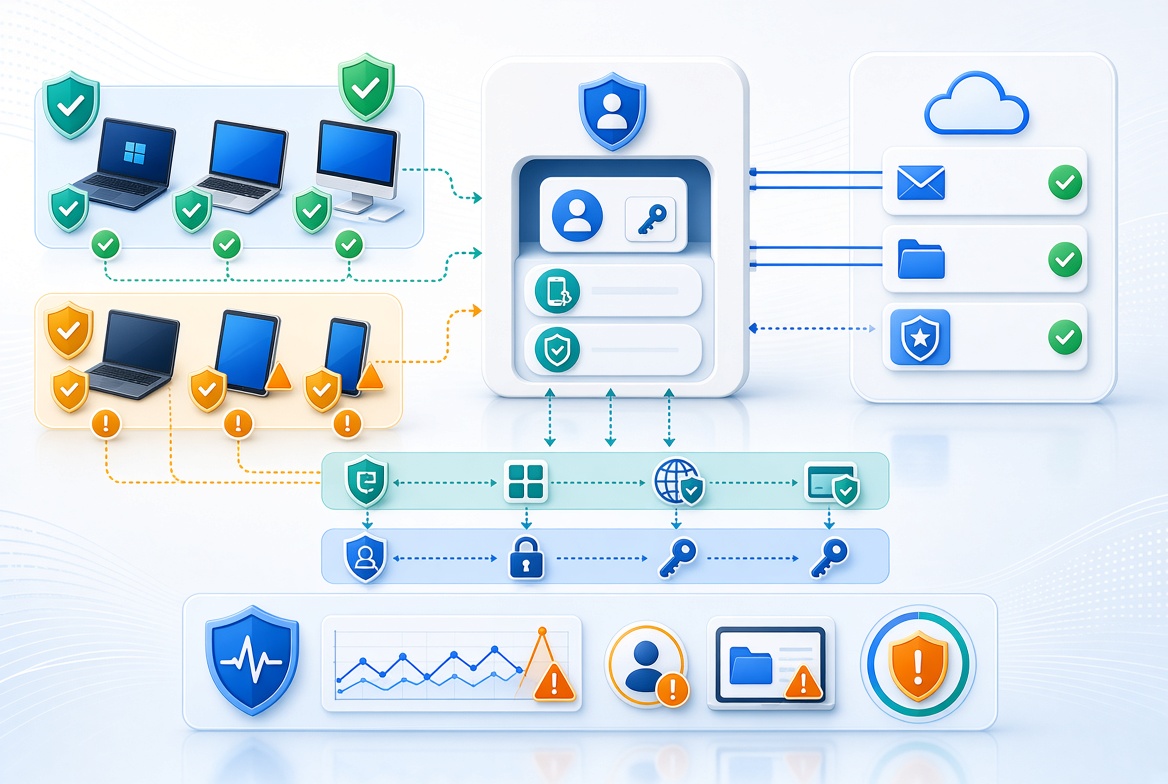
Fully managed, fully compliant devices are the ideal. In most environments a meaningful percentage of endpoints are only partially managed, contractor devices, or simply not enrolled. These are the controls that still move the needle in that reality:
- Require strong MFA and compliant device (or app protection) for any access to email, files, or admin portals. Conditional Access is still the highest-leverage control even when the device itself is not fully enrolled. The goal is to make the unmanaged device painful for the attacker and tolerable for the legitimate user.
- Push attack surface reduction rules and SmartScreen / web filtering to every Windows device you can reach, even if it is not fully Intune-managed. Many of these rules can be deployed via script, GPO, or the limited MDM channel that still exists on those devices. They stop a surprising amount of commodity malware.
- Assume local admin is already present and focus on credential isolation. Windows LAPS (or an equivalent) plus just-in-time admin elevation for the tasks that truly need it is more realistic than trying to remove local admin everywhere. Monitor for the creation of new local accounts and for the use of known admin tools.
- Make EDR coverage non-negotiable for any device that touches company data. If a device cannot run the EDR agent, it should not be able to access the most sensitive systems. This is often easier to enforce through network or identity controls than through device enrollment.
- Watch for the “new device + sensitive data” pattern. A device that has never been seen before and is immediately downloading large amounts of files or connecting to admin portals is worth a human look, regardless of its management state.
The organizations that do best here stop trying to achieve 100 % full management and instead apply the strongest possible identity and network controls to the devices they cannot fully manage. The difference in incident volume is usually obvious within a quarter.